





Know when an identity is compromised
AURA watches your Microsoft 365 audit logs around the clock and tells you, in real time, when a company account is compromised or used in an anomalous way. All data stays on our servers in Switzerland

BENEFITS
Protect the identities behind your Microsoft 365
Real-time visibility into your accounts, without building an in-house SOC
- Real-time detection.
Audit logs from your tenant are collected continuously and analysed as they arrive, so a compromised account is flagged while it is still being used.
- Nothing to install, everything in Switzerland.
AURA connects to the Microsoft 365 APIs, with no network sensors and no agents on the endpoints. Your data is processed and stored exclusively on EXYS servers in Switzerland.
- Alerts you can act on.
Every rule looks at one thing only and can be explained in a single line. An analyst understands the alert without opening the Microsoft documentation.
- Tuned to your data.
Rules are calibrated to the real activity of your tenant, not to generic thresholds, to keep false positives low.
- Managed by EXYS analysts.
Alerts are deduplicated, enriched and handed to our analysts, who follow up on them for you. Confirmed cases become tickets with an owner and a documented outcome, and we notify you by email, Slack or webhook.
- Collection health check.
If the audit logs stop arriving, AURA tells you. Silence never gets mistaken for safety.
FEATURES
Three scenarios, fully covered
Someone breaking in, someone taking data away, someone preparing to come back

- Suspicious sign-ins.
- Impossible travel, sign-ins from unusual countries, password spraying, legacy authentication that bypasses MFA and token theft through adversary-in-the-middle (AiTM) attacks.
- Mail and data exfiltration.
- Suspicious forwarding and inbox rules, mass deletion or mass sending of emails, anomalous downloads and sharing on SharePoint and OneDrive.
- Persistence.
- FullAccess permissions on other mailboxes, mailbox auditing turned off, new apps or changed credentials on approved apps, OAuth grants and modified MFA methods.
- Full Microsoft 365 coverage.
- Entra ID, Exchange Online, SharePoint, OneDrive and Teams audit logs, the email message trace and Microsoft Graph data. Sign-in logs require Entra ID P1 or higher; full risk detections and risky users require Entra ID P2.
- Threat intelligence enrichment.
- Every event is geolocated and enriched with IP and domain reputation before it is analysed.
- Dashboards and reports.
- Ready-made, customisable dashboards, free-form log searches with a dedicated query language and scheduled PDF reports generated automatically.
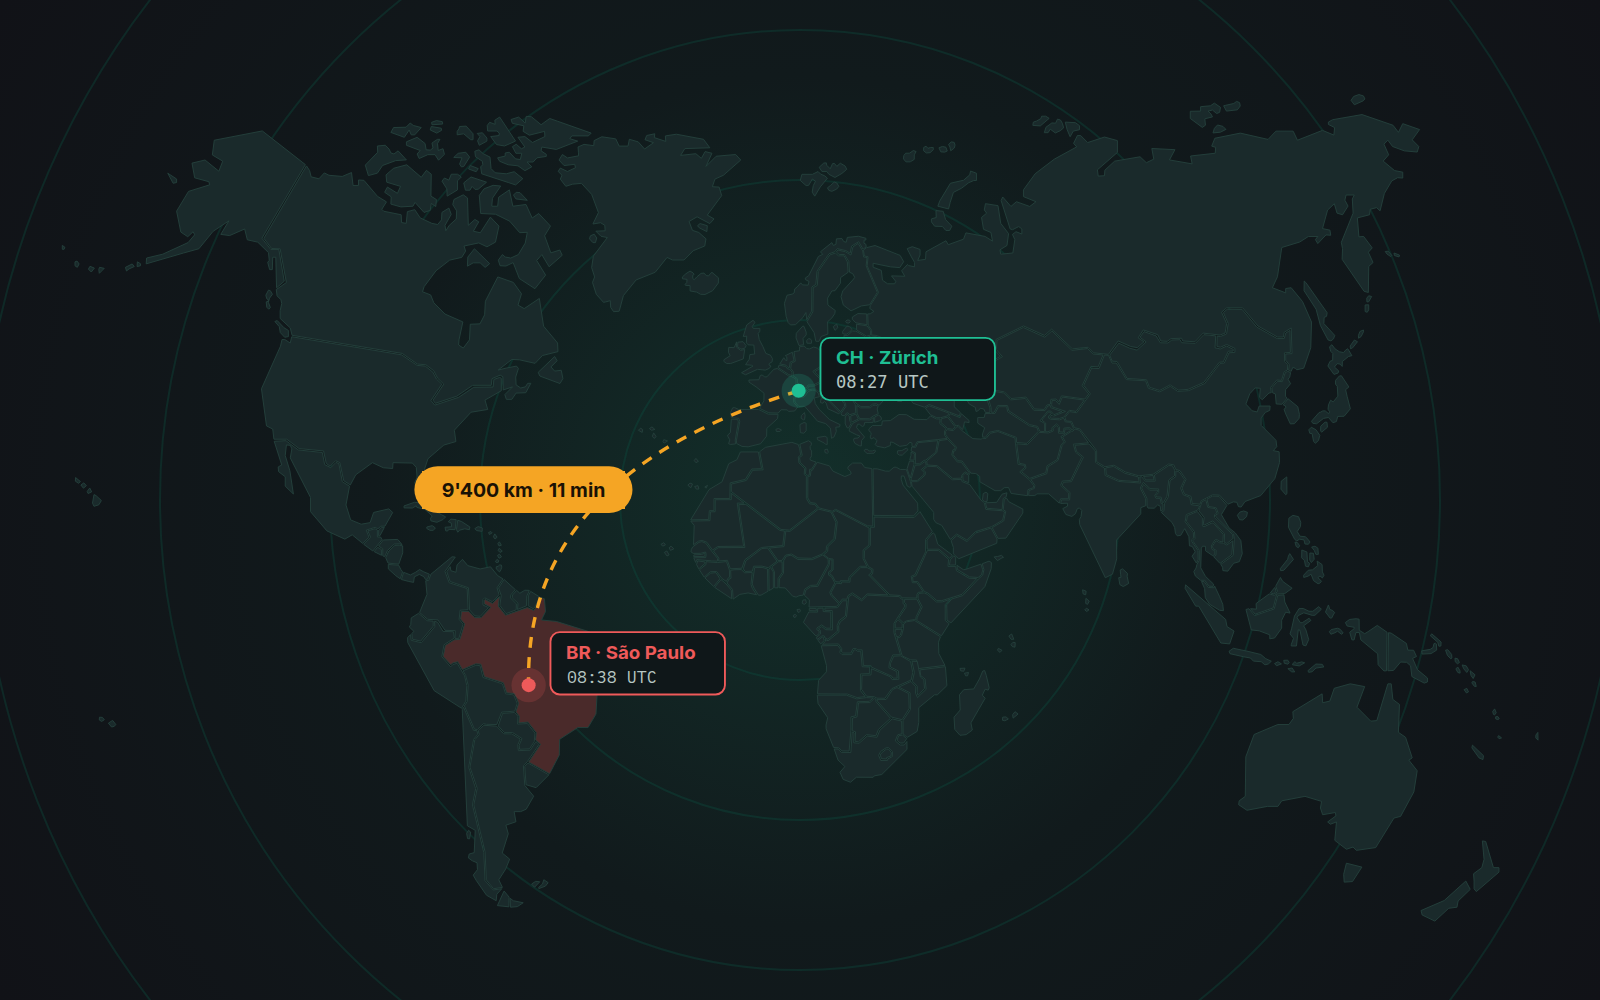
A sign-in that cannot be real
The same account signs in from Zurich and, 11 minutes later, from São Paulo, in the same session: no one can travel 9,400 km that fast. AURA geolocates every sign-in and flags impossible travel, sign-ins from unusual countries and password spraying while the session is still open.
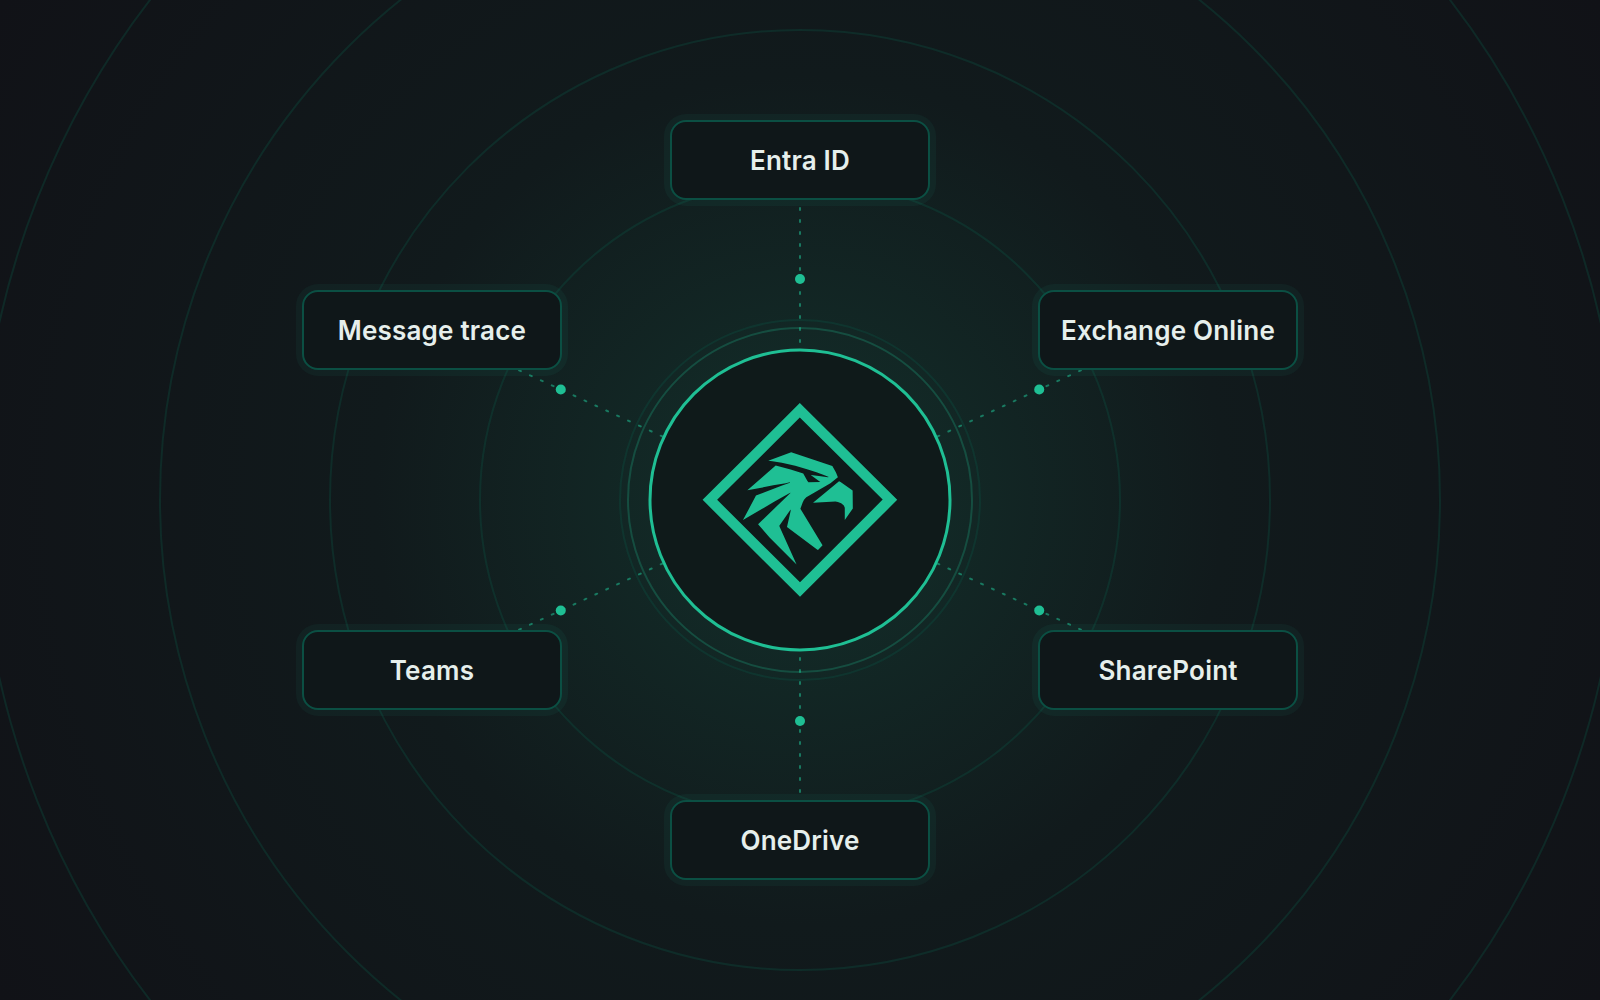
Your whole Microsoft 365, in one place
Entra ID, Exchange Online, SharePoint, OneDrive and Teams audit logs, plus the email message trace, all flow into AURA through the Microsoft 365 APIs and stay on our servers in Switzerland. No sensors and no agents: you connect the tenant and the monitoring starts.
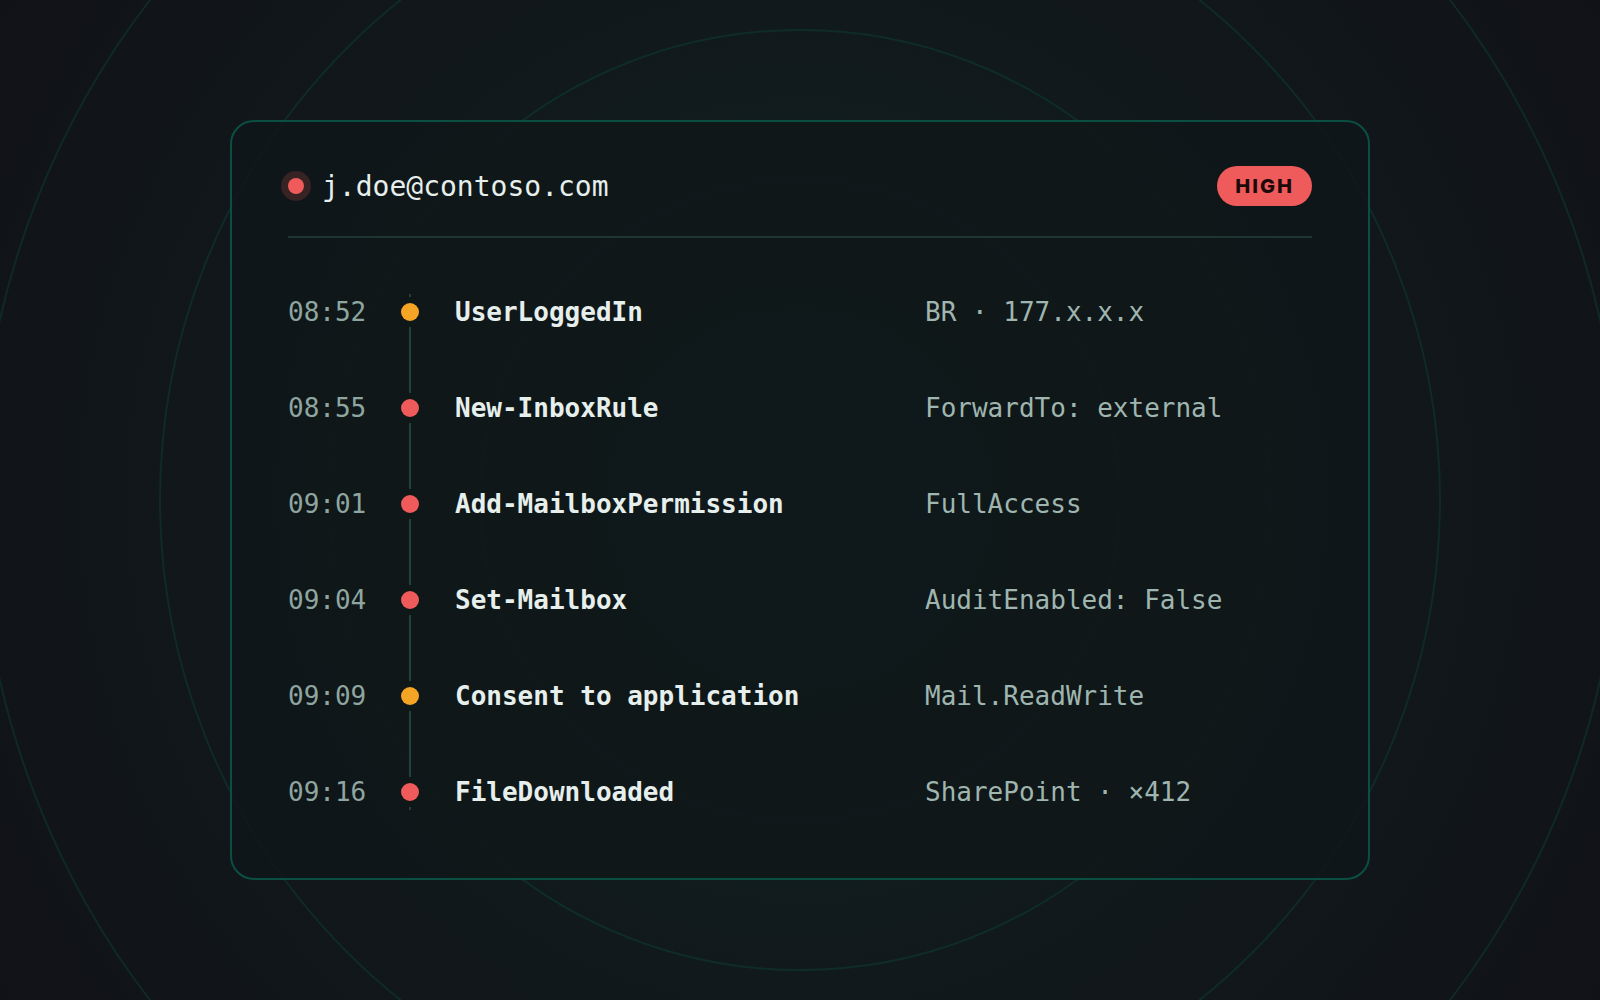
From the first sign-in to the stolen data
After an account takeover, attackers make themselves at home: they forward mail to external addresses, grant themselves access to other mailboxes, turn off auditing and download files in bulk. AURA recognises each of these steps and lines them up on a single timeline, so our analysts see the whole attack, not just one alert.
Want to know more?
Contact us to book a demo or ask further questions about protecting your Microsoft 365 identities. You can also find more information by downloading our free product flyer.