





Know your weak spots
Vulnerability assessment for Swiss SMEs
Ocelot is a vulnerability assessment and asset inventory tool from EXYS in Bioggio, Ticino. An appliance plugged into your network finds undocumented devices, insecure configurations and known vulnerabilities through scheduled scans, and produces reports for management and auditors.

Vulnerability assessment with scheduled scans
Ocelot stays connected and scans on a schedule, with several recurring scans timed to run outside business hours. Every service it finds is matched against the public CVE database and given a severity, so a new device or a new vulnerability shows up in the next report instead of the next audit.
Asset and software inventory
Every active device Ocelot can reach is listed with its address, MAC vendor, hostname, operating system and open ports. An agent on each workstation adds the installed applications and their versions, so an outdated browser appears in the same report as an unpatched server.
Reports for audits and management
After each scan Ocelot shows an overview, then emails the full report: executive summary, inventory tables, findings with risk levels, technical detail and recommendations. The history shows when each problem was found and when it went away, which is what an auditor or a data protection review asks for.
BENEFITS
Know your security posture
Because prevention is the best defence
- Improved visibility
Knowing your network is the first step towards securing it. Detect undocumented devices and network misconfigurations in a few clicks!
- Vulnerability management
Reduce risk: know immediately when obsolete or insecure devices are present in your network.
- Auditing
Asset inventories and detailed vulnerability reports simplify audits.
FEATURES
Flexible and powerful
Let Ocelot do the heavy lifting for you

- Flexible scheduling.
- Scheduled scans detect new vulnerabilities as soon as they appear. Configure once and let Ocelot do the rest.
- Exclusion management.
- Sensitive devices? Easily remove them from vulnerability scans to avoid downtime.
- Detailed reporting.
- See the state of your network at a glance. Executive summary, inventory tables, customised findings, technical details: all are included.
- Endpoint analysis.
- Quickly build an inventory of installed software and other endpoint configuration details.
- Network score.
- See how your network improves as you make changes to enhance your security posture.
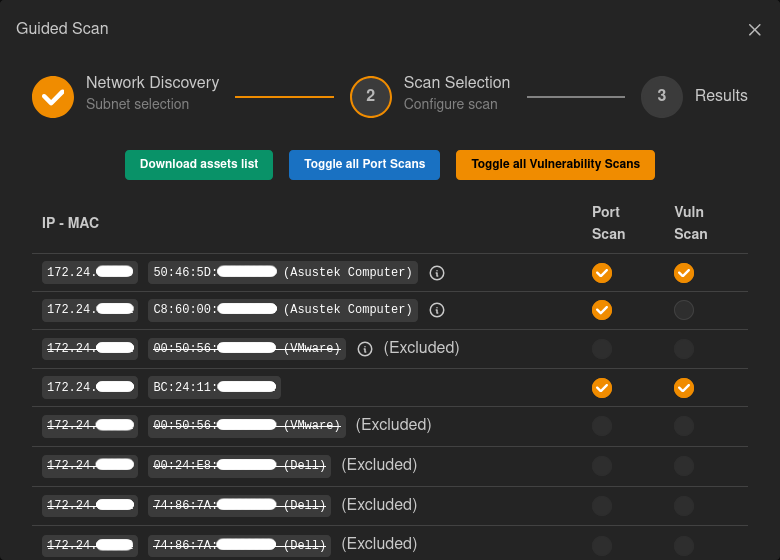
Fine-grained scan configuration
Configure exactly what needs to be scanned and when. A lightweight port scan allows you to see what's on your network, while a full vulnerability scan detects potential risks in your network. You can schedule multiple recurring scans, so business-critical devices can be scanned outside working hours, for extra peace of mind.
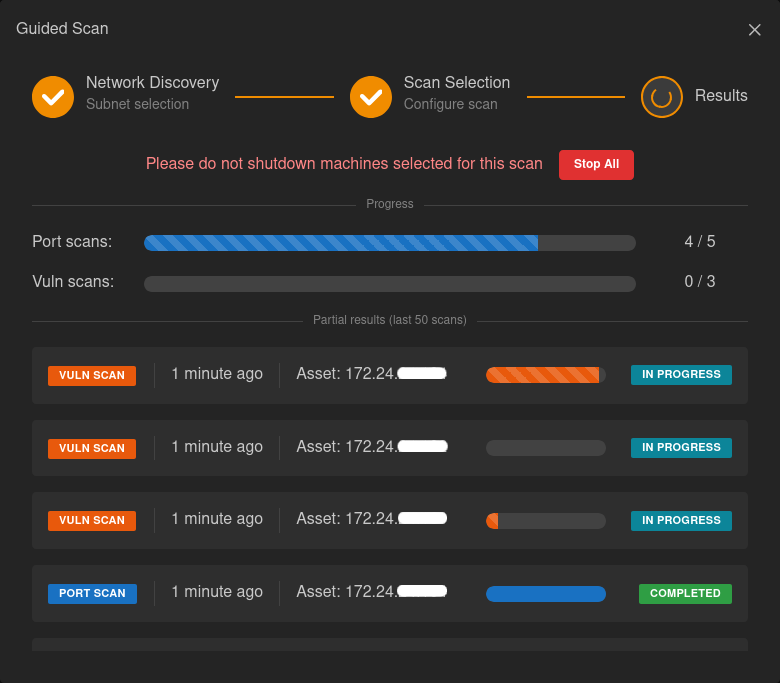
Set it and forget it
Once configured, Ocelot works autonomously and makes full use of multi-core processing to run scans in parallel as fast as possible. Once a scan completes, a quick overview is immediately presented, while a customised report will be emailed to you after a few days.
Frequently asked questions
What is a vulnerability assessment?
A vulnerability assessment is a systematic check of the devices and software on your network for known weaknesses, such as missing patches, outdated versions and insecure configurations. Ocelot does it automatically: it lists what is on the network, matches each service against the public CVE database and ranks the findings by severity.
What is the difference between a vulnerability assessment and a penetration test?
A vulnerability assessment looks for known weaknesses across the whole network, regularly and automatically. A penetration test is a manual attack simulation, in which a specialist tries to exploit weaknesses to see how far an attacker could get. Ocelot does the vulnerability assessment; EXYS also carries out penetration tests, so contact us if you need one.
How often should you run a vulnerability scan?
New vulnerabilities are published every day, so a single scan quickly goes out of date. With Ocelot you set recurring scans, for example every week, and each report shows what has changed since the last one.
Can the scans slow down or block systems?
Plugging Ocelot in changes nothing on the network. Sensitive devices can be left out of the vulnerability scans, and scans can be timed to run outside business hours, so nothing critical is disturbed.
Does a vulnerability assessment help with NIS2 and the revised FADP?
Both ask companies to know their systems and manage their risks. Ocelot's reports document what is on the network, which vulnerabilities were found and when each one was fixed: exactly the record an auditor or a data protection review asks for. That makes Ocelot an essential tool for compliance.
Where is the scan data kept?
The scan data stays on the appliance in your network. Only the reports are stored on EXYS servers in Switzerland.
Want to know more?
Contact us to book a demo or ask further questions. You can also find more information by downloading our free product flyer.