





See everything that matters
Managed detection and response (MDR) and SOC for Swiss SMEs
Kondra is a 24/7 managed detection and response (MDR) and SOC service from EXYS in Bioggio, Ticino. It combines a SIEM, which collects and analyses logs and events, with NDR, the analysis of your network traffic, and integrates with endpoint (EDR) tools. Your data stays in Switzerland, on an appliance in your own network.

SIEM: all your logs in one place
Kondra collects the logs of firewalls from several vendors, Microsoft 365, Windows events, the network and IDS, plus custom sources on request, and indexes them as they arrive. Every event is searchable, and retention is set per customer, with integrity checks and backups for compliance audits.
NDR: network traffic analysis
The appliance reads traffic passively from a switch mirror port, across more than 20 network protocols. Unusual connections, misconfigured hosts and data leaving the network show up even on machines with nothing installed.
A SOC watching 24/7
Detection rules and threat intelligence turn the volume into alerts, and EXYS SOC analysts work through them 24 hours a day. For each incident the SOC opens a case with the logs and indicators of compromise (IoC) attached, and the forensic report is written from the same data.
BENEFITS
Complete control over your network
The next level of monitoring for your company
- Real-time monitoring.
Everything that happens in your network is indexed in real time and becomes instantly searchable.
- Inventory.
Kondra includes tools to help you keep an up-to-date inventory of every endpoint in your network, and of every application installed on each endpoint.
- Incident response.
When a security incident happens in your network, Kondra helps you trace the events that led to the incident and decide what action to take.
- Compliance.
Custom data-retention policies allow you to balance costs and compliance with specific legal requirements.
- Alerting.
Thanks to an extensive, ever-growing set of anomaly detection rules, you are the first to know if something anomalous happens inside your network.
FEATURES
Full-featured detection and response
The best coverage you can get for your company

- Scalable.
- The appliance comes in different sizes, depending on the number of endpoints on your network. Scaling to match your network is not an issue.
- Multi-protocol.
- 20+ network protocols supported natively and constantly updated.
- Endpoint monitoring.
- Ombra, our custom endpoint agent paired with Kondra, enhances monitoring and inventory management with detailed information, giving you a complete picture of your assets.
- Active Directory monitoring.
- Get an overview of Active Directory (AD) users, groups, group policies and Organizational Units. Easily track changes to AD objects.
- Multi-layer detection.
- Signature-based intrusion detection, correlation rules, command-and-control detection, behavioural anomaly analysis and machine learning work side by side: a threat missed by one layer is caught by another.
- Security posture and risk.
- Kondra continuously checks your environment for weak configurations and risky practices, audits Active Directory down to privilege-escalation paths and gives every host a risk level, so the most urgent ones are handled first.

Advanced visualisations
Simple visualisations cover most use cases. But sometimes, “simple” is not enough. That's why our dashboards include advanced visualisations in which anomalous behaviour clearly stands out.
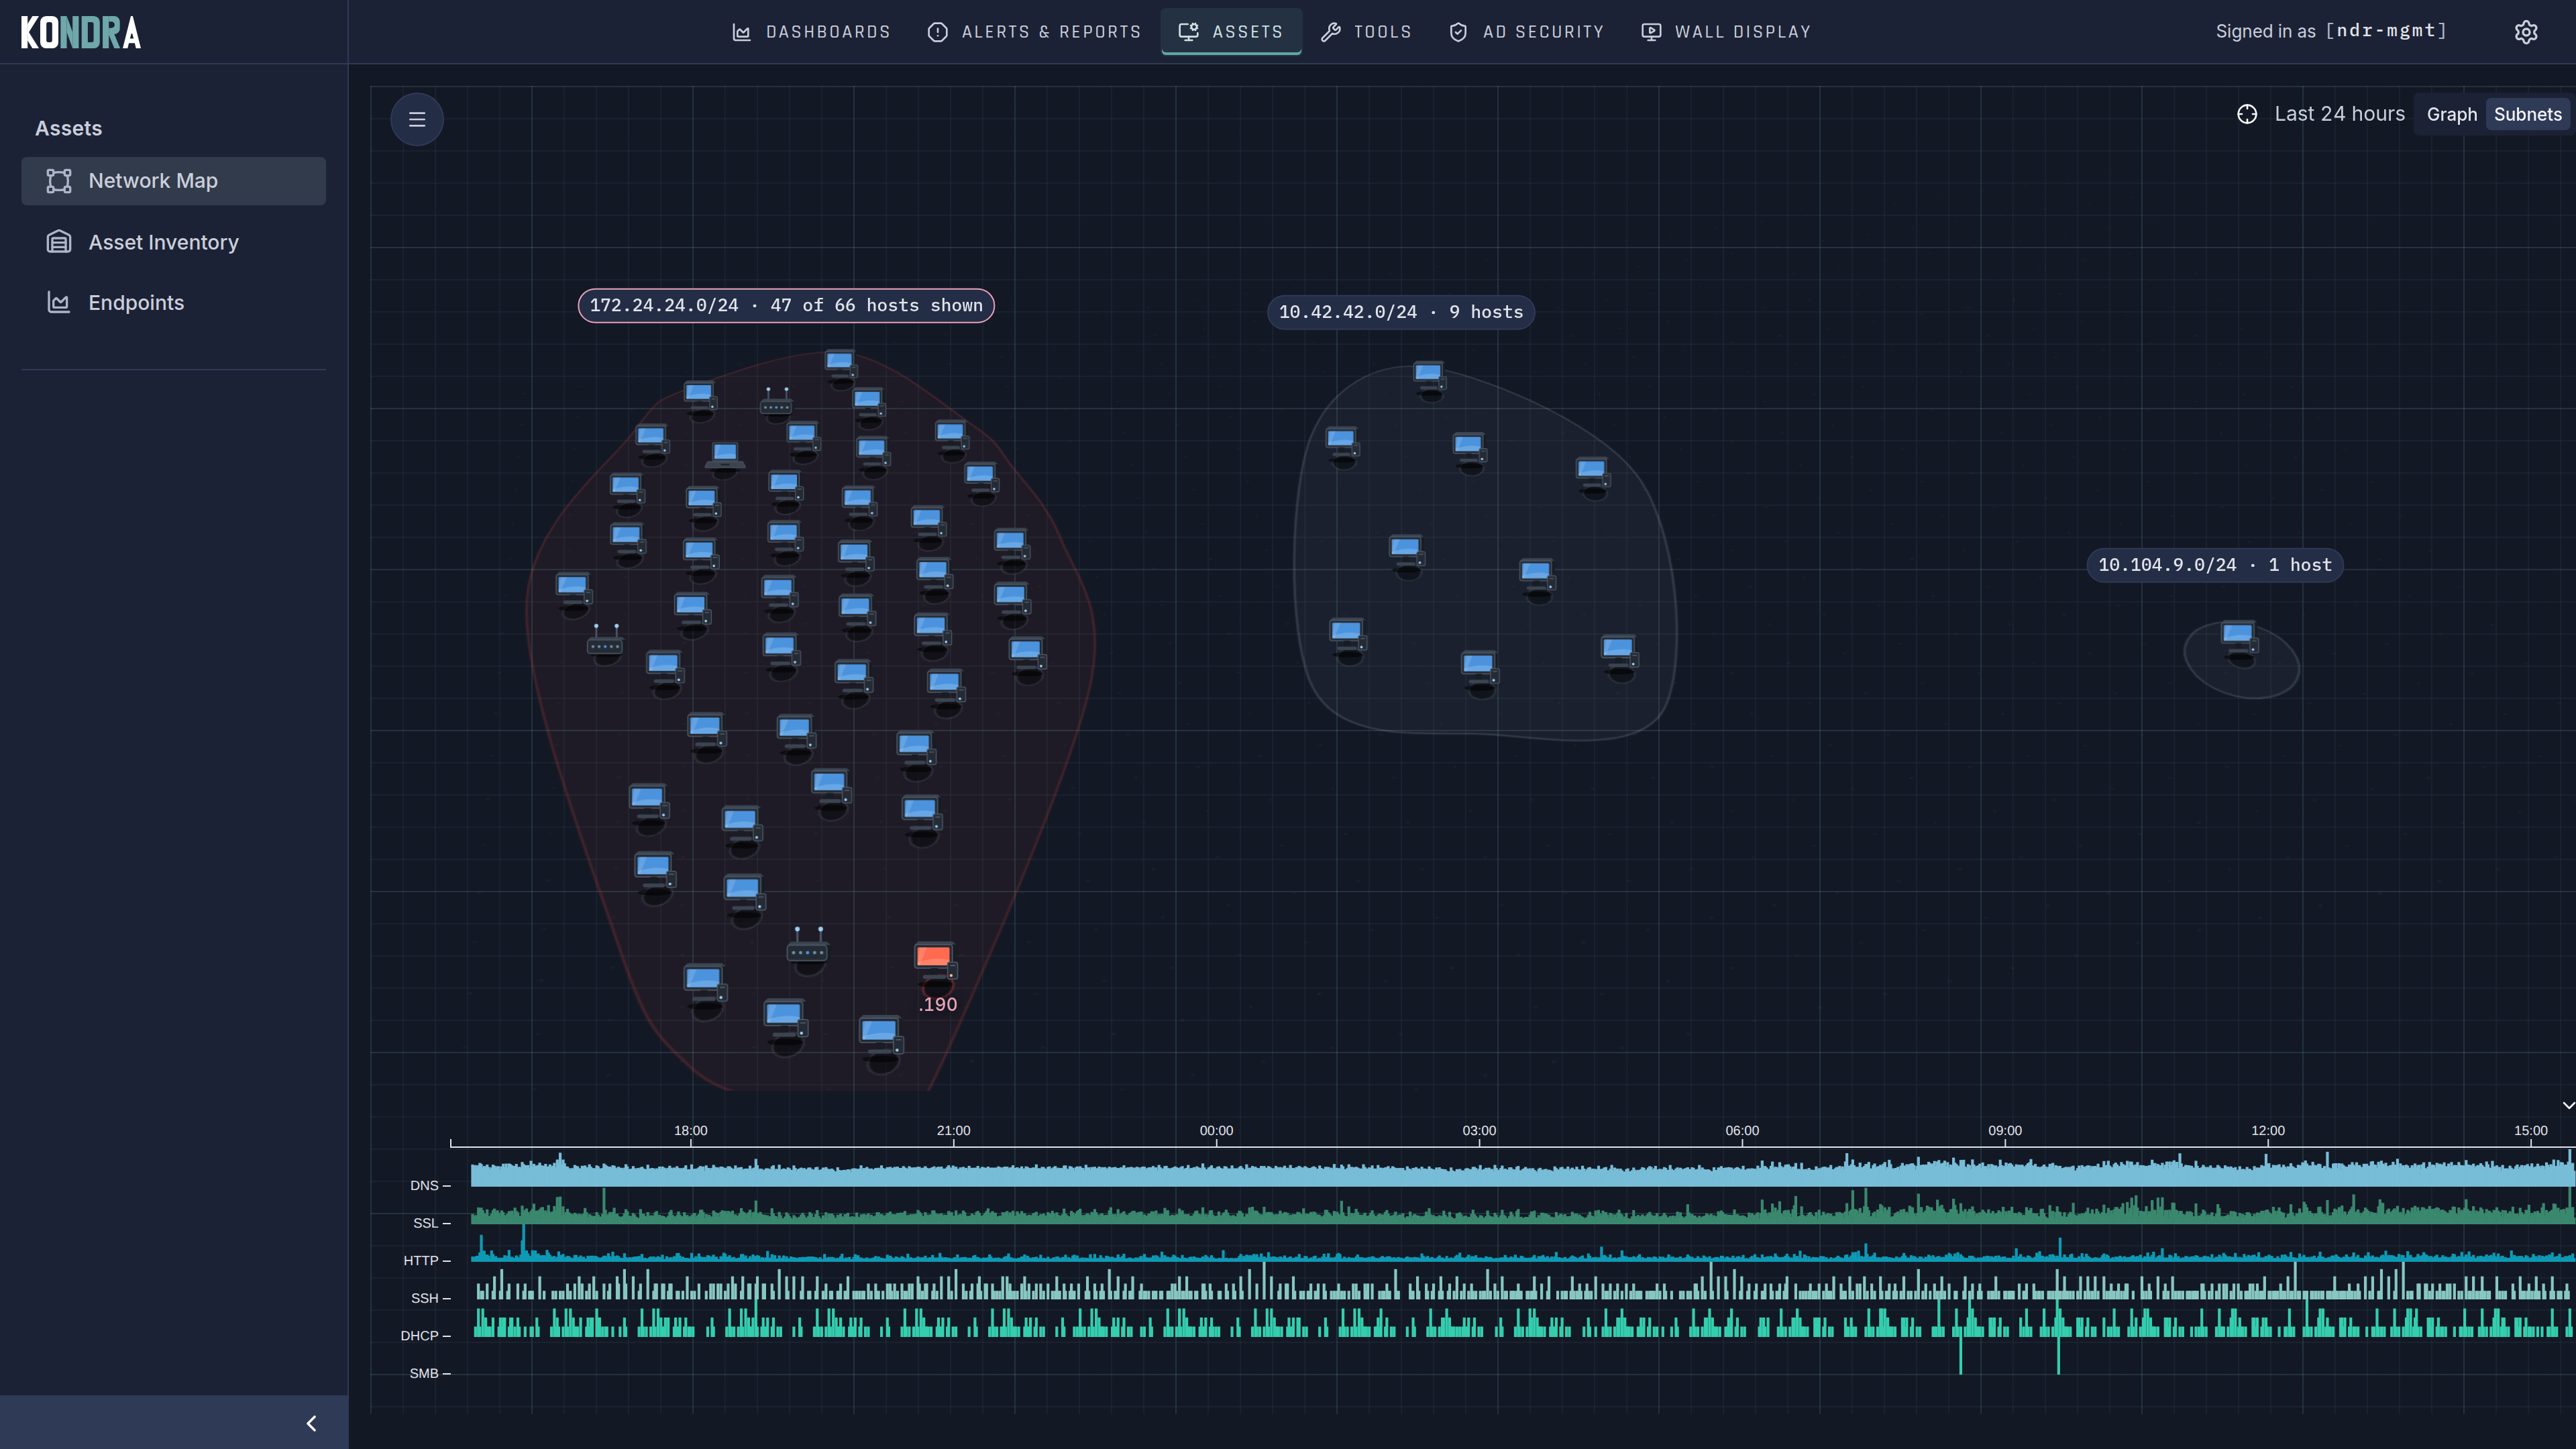
Map your network
Kondra helps you get a clear view of your network, where problematic hosts are easy to spot, so you can fix issues with ease.

VPN/Firewall
As the main points of entry into your company, firewall and VPN solutions are a crucial part of attack surface monitoring. Kondra supports a growing number of modern firewalls and VPNs, and if yours is not included, we will gladly integrate it.
Frequently asked questions
What is an MDR service?
MDR (managed detection and response) is a service in which an external team watches your network, detects threats and helps you respond to them. With Kondra, EXYS SOC analysts do this 24 hours a day, so you do not need to hire and train your own security team.
What is the difference between SIEM and NDR?
A SIEM collects and correlates the logs produced by firewalls, servers, Windows and Microsoft 365. NDR analyses the network traffic itself, so it also sees devices that produce no logs or have nothing installed. Kondra does both.
Is the SOC in Switzerland?
Yes. The EXYS SOC is in Switzerland. Your data stays on an appliance in your own network: the analysts look at it there, without copying it out of your company.
Is Kondra suitable for SMEs?
Yes, it is built for them. The appliance is sized to the number of endpoints in your network, and the EXYS SOC provides 24/7 monitoring, so you do not have to build a SOC of your own.
Want to know more?
Contact us to book a demo or ask further questions. You can also find more information by downloading our free product flyer.